Category

Blog

Home / Blog
ISO 42001 Adoption Trends Among SMEs
Article, Blog, News

ISO 42001 Adoption Trends Among SMEs

AI policy is quickly becoming a commercial issue, not just an IT discussion. The most significant ISO 42001 adoption trends among SMEs are being driven by a simple question from customers, buyers and directors: can you show that AI is being used responsibly, securely and under control?

For smaller businesses, that question may arise when using generative AI to draft proposals, analyse customer data, support recruitment or automate routine work. It may also arise when an organisation sells an AI-enabled product or relies on software suppliers that do. ISO/IEC 42001 provides a structured way to manage those risks without turning every AI project into a lengthy compliance exercise.

Why ISO 42001 adoption is gaining momentum

ISO/IEC 42001 is the international standard for AI management systems. It gives organisations a framework for setting rules, assigning responsibility, assessing AI-related risks and showing that controls are reviewed over time. It does not ban AI or prescribe one piece of software. Instead, it helps a business make informed, accountable decisions about how AI is selected, used and monitored.

Adoption is growing because AI use has moved beyond experimentation. A team member may use a public AI tool to prepare marketing copy, summarise meeting notes or help with code. Each use can create questions about confidential information, accuracy, copyright, bias, data protection and customer commitments. Businesses do not need to stop benefiting from these tools, but they do need clear boundaries.

Customer expectations are also changing. Larger organisations, public-sector buyers and regulated clients increasingly expect suppliers to explain their approach to information security, privacy and emerging technology risks. ISO 42001 can provide a credible, organised response, particularly where AI is central to the service being supplied.

The trend is strongest in technology, software, professional services, recruitment, financial services support, healthcare suppliers and businesses handling large volumes of customer information. However, any SME using AI in decisions that affect people, money, safety or sensitive data should consider whether a formal management system is proportionate.

ISO 42001 adoption trends are not just about certification

Many organisations begin by searching for certification, but the practical value lies in the system behind the certificate. A good AI management system gives staff straightforward instructions and gives directors better visibility of where AI is being used. It replaces informal assumptions with evidence-based controls.

For an SME, this does not need to mean a large compliance department or hundreds of documents. The scale of the system should reflect the scale, purpose and risk of the AI activity. A marketing agency using AI to produce first drafts needs different controls from a software provider whose platform makes automated recommendations to customers.

In practice, businesses are focusing on a few core areas. They are creating an inventory of AI tools and use cases, setting approval rules for new tools, defining what information must never be entered into public platforms, and establishing checks for outputs that could be inaccurate or discriminatory. They are also making someone accountable for oversight, even where that person has several other responsibilities.

This proportionate approach matters. Over-engineering the system can slow down adoption and frustrate employees. Under-controlling it can expose the business to avoidable errors, customer complaints or contractual problems. ISO 42001 helps organisations find a workable middle ground.

The move from AI policies to managed evidence

An AI policy is a useful starting point, but it is rarely enough on its own. Buyers and auditors may ask how the policy is put into practice, who approves higher-risk uses, whether staff have been trained, and what happens when something goes wrong.

This is where ISO 42001 is different from a one-page policy. It encourages organisations to establish objectives, assess risks and opportunities, maintain documented information, monitor performance and improve their approach. The aim is to demonstrate control rather than simply state good intentions.

For example, an organisation might allow staff to use approved AI tools for drafting internal content, provided no personal data, client-confidential information or commercially sensitive material is uploaded. A manager could review customer-facing outputs, while a quarterly review checks whether new tools have been introduced and whether the rules remain suitable. That is a manageable control process, and it creates evidence that the business is actively governing its AI use.

There is a trade-off. More evidence can make it easier to demonstrate compliance, but excessive paperwork creates work with little operational benefit. The most effective systems use concise procedures, practical registers and records that fit into existing workflows.

Integration is shaping the next phase of adoption

One of the clearest ISO 42001 adoption trends is integration with existing management systems. SMEs that already work to ISO 9001, ISO 27001 or ISO 22301 are often well placed to add AI governance because they already understand risk registers, internal audits, corrective actions and management reviews.

ISO 27001 is particularly relevant where AI tools process business information. Information security controls can help address access, supplier due diligence and data handling, while ISO 42001 adds the governance needed for AI-specific risks such as bias, explainability, human oversight and the quality of AI-generated outputs.

ISO 9001 can also provide a useful foundation. Where AI affects the delivery of products or services, quality processes help ensure outputs are checked, customer requirements are understood and mistakes are dealt with consistently. Rather than building separate systems, an integrated approach can reduce duplication and make ongoing management more affordable.

For businesses starting from scratch, it may still make sense to begin with ISO 42001 alone. The right route depends on your customer requirements, the sensitivity of the information involved and whether AI is central to your operations. A company using AI occasionally for administration may need a focused policy and risk assessment first. A company selling AI-enabled services may benefit from implementing the full standard sooner.

What SMEs should do before pursuing ISO 42001

The fastest route is not to begin with documents. Begin with an honest view of current AI use. Speak to the people doing the work, not only senior management. Informal use is common, and a system can only manage risks that the business has identified.

Start by mapping the tools in use, their purpose, the data involved and the people affected by each use case. Then assess what could go wrong. Could an inaccurate output reach a customer? Could confidential data be exposed? Could an automated decision disadvantage an applicant, employee or customer? Could a third-party provider change its terms or model without your knowledge?

Next, decide what level of control is appropriate. Lower-risk uses may only need approved-tool guidance and staff awareness. Higher-risk uses may need formal approval, testing, documented human oversight, supplier checks and incident procedures. Make accountability clear, including who can approve a new AI application and who reviews its performance.

Training deserves particular attention. Staff should know that AI outputs can be persuasive and still be wrong. They need practical examples of permitted and prohibited use, along with a simple route for raising concerns. Rules that are hard to understand will be ignored, especially in busy small teams.

A digital-first certification process can keep this work focused. ISO-Cert Online supports SMEs with guidance, templates and remote assessment, helping them build a system that reflects their actual risks rather than a generic compliance file.

When waiting may be the sensible choice

Certification is not automatically the right first move for every organisation. If a business has not yet decided how it will use AI, or is only trialling a low-risk tool with no sensitive data, it may be better to establish basic governance before committing to certification. The same applies where senior leadership has not assigned ownership for AI decisions.

However, waiting should not mean doing nothing. A short AI use policy, a tool register and clear data-handling rules can provide an immediate foundation. They also make future ISO 42001 implementation quicker when a customer request, tender requirement or growth plan makes certification commercially valuable.

The businesses best placed to benefit from AI will not necessarily be those using the most tools. They will be the ones that can use AI confidently, explain their controls clearly and show customers that innovation is being managed with care.


Ready to get started?

Contact us today on +44 (0)333 014 7720 or email info@isocertonline.net for a free consultation. You can also get a quote online in minutes.

Don’t let cost hold you back from achieving ISO certification. With ISO-Cert Online, management systems certification is affordable for every business.

Posted on Google Google
Andrew Jackson profile picture
Andrew Jackson
4 September 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
I would like to provide the highest of recommendations to ISO-Cert Online Ltd. An extremely efficient and detailed service is provided and with all of the ISO Certifications which are required. The Integrated Management System that was provided to my Company is extremely thorough and already providing extremely great value and improvements to my Company. Their portal is also a great service to use currently and with regards to re-certification. I am greatly enjoying using the templates that were provided and they are extremely detailed. Claire and Steve are additionally extremely personable and highly responsive to any queries. ISO-Cert Online Ltd also provides great value for money and I am extremely glad that I chose to use their Company for ISO 9001 and 14001 certification.
Posted on Google Google
Tim Prestwood profile picture
Tim Prestwood
30 April 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Our experience with ISO-Cert Online has been exceptional. Completing our ISO 9001 and 14001 certifications felt like a daunting task at the start, but the team made the entire process straightforward and manageable for us at Virdis Chemicals. Steve and Claire are extremely professional and supportive partners. They consistently go out of their way to explain complex processes and identify clear areas where we can improve our systems. We truly appreciate their guidance and the clear roadmap they provided for our assessment. If you are looking for expert support with ISO certification, I cannot recommend them highly enough.
Posted on Google Google
Info MK Medicals UK profile picture
Info MK Medicals UK
12 February 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
ISO-Cert Online Ltd have been excellent to work with. Their team is consistently professional, responsive, and supportive, helping us keep our ISO certifications fully up to date with confidence. They are always available to assist, provide clear guidance, and maintain outstanding customer relations. A reliable and knowledgeable partner that we highly recommend. — MK Medicals (UK) Ltd
Posted on Google Google
Christian Hallam profile picture
Christian Hallam
3 February 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
After purchasing ISO 9001 & ISO 14001 certification for my company. Claire & Steve took the time to explain everything and support us through the process of creating and applying the new management system. Great value for money. ISO Cert Online helped to simplify what can be a complicated and confusing process. Thank you
Posted on Google Google
NIkos Xiros profile picture
NIkos Xiros
3 November 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Great company with excellent service. They’re always responsive, helpful, and ready to answer any questions you may have!
Posted on Google Google
Hannah Van-Der-Linden profile picture
Hannah Van-Der-Linden
24 June 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
We started looking at implementing ISO 9001 two years ago, and after numerous emails with Claire, we finally decided to embark on our ISO 9001 journey. We are now three months in and extremely grateful for the support and advice we've received. Steve has been instrumental in guiding us through the process. We’re looking forward to a long and successful working relationship with Steve and the team. - Greenway & Partners Ltd
Posted on Google Google
Aleks Dimitrova profile picture
Aleks Dimitrova
13 June 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
extremely quick and efficient, knowledgeable and responsive. Lovely Team, great company!
Posted on Google Google
Ali Madani profile picture
Ali Madani
5 November 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Steve's service was absolutely amazing, extremely fast turnaround, the save me a lot of hassle and time and they are so efficient that I couldn't recommend this company enough, I can only describe their service in one word FANTASTIC Thank you Steve and your team. Ali Madani EezzeE Ltd
Posted on Google Google
Elaine B profile picture
Elaine B
22 October 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Very professional service, easy to work with and delivered exactly what we asked for in the time frame quoted.
Posted on Google Google
Ged Riley profile picture
Ged Riley
18 October 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Great support on all things ISO
How Does ISO 42001 Apply to Companies Using AI Tools?
Article, Blog, News

How Does ISO 42001 Apply to Companies Using AI Tools?

A staff member pastes customer information into a public chatbot. A recruitment tool filters out an applicant without anyone being able to explain why. A marketing team publishes AI-written claims that have not been checked. These are not distant enterprise problems. They are everyday decisions that show why companies ask how ISO 42001 applies to companies using AI tools.

ISO 42001 is the international standard for an Artificial Intelligence Management System, or AIMS. It gives organisations a practical framework for governing AI properly: setting responsibilities, understanding risks, checking outcomes and improving controls over time. For UK SMEs, it is not about turning every employee into a data scientist. It is about using AI in a controlled, accountable way that customers, staff and regulators can trust.

How ISO 42001 Applies to Companies Using AI Tools

ISO 42001 can apply whether your business builds AI products, embeds AI into software, or simply uses third-party tools such as generative chatbots, transcription platforms, HR screening systems, customer-service assistants and analytics packages. The depth of your system should reflect the scale, purpose and risk of your AI use.

That distinction matters. A small design agency using an AI assistant to produce first drafts does not need the same level of technical assessment as a software firm deploying an AI model that influences lending, medical decisions or recruitment. But both businesses need clear rules around data, human oversight, accuracy and accountability.

The standard asks a simple commercial question: can you demonstrate that your organisation understands how AI is being used and has proportionate controls in place? If a client, tender assessor or insurer asks who approved an AI tool, what data it receives, or how its output is checked, you should have a reliable answer rather than a collection of informal habits.

It covers AI use, not just AI development

Many firms assume ISO 42001 is only relevant if they create algorithms. In reality, a company can be an AI user and still carry meaningful responsibility. If your team enters personal, confidential or commercially sensitive information into a tool, you need to know where that data goes, what the supplier does with it and whether the tool is suitable for the task.

Likewise, if employees rely on AI-generated answers to advise customers, write policies, make personnel decisions or assess compliance, the business remains accountable for the result. The fact that a tool produced the output does not remove the need for professional judgement.

ISO 42001 helps turn these concerns into a managed process. It does not ban useful tools. It helps you decide where they are appropriate, where human approval is required and where their use should be restricted.

What an AI management system looks like in practice

An AIMS should fit the way your business works. For an SME, this is usually a focused set of policies, registers, assessments and review activities rather than a large corporate manual.

Start by defining the scope. You might cover all AI tools used across the business, or begin with a higher-risk area such as customer data, HR, finance or software delivery. A sensible scope is clear about which teams, processes, systems and locations it includes.

You then need an AI inventory. This is a current record of the tools in use, their intended purpose, the supplier, the types of data involved, the person responsible and the level of risk. It often reveals more than expected. Staff may be using browser-based tools under individual accounts that were never assessed or approved.

For each significant use case, carry out an impact and risk assessment. Consider not only cyber security and data protection, but also inaccurate outputs, bias, lack of explainability, intellectual property concerns, unsafe advice and damage to customers or your reputation. The aim is not to eliminate every risk. It is to identify the realistic ones and choose controls that make sense.

For example, an AI tool used to summarise internal meeting notes may require restricted data inputs and a quick human check. An AI system that ranks job applicants needs much closer scrutiny, defined approval authority, testing for unfair outcomes and a clear route for people to challenge a decision.

The controls SMEs usually need

The right controls depend on your risk assessment, but most companies using AI tools will need a combination of documented rules and day-to-day checks. These may include an acceptable-use policy, approved-tool process, data-handling guidance, human-review requirements, staff training, supplier assessments and an incident process for when something goes wrong.

Staff awareness is particularly valuable. Employees should know not to enter confidential client information into unapproved tools, treat generated content as factual without checking it, or use AI to make sensitive decisions without authorised oversight. A short, clear policy that teams understand is more effective than a lengthy document left unread.

ISO 42001 also expects senior management involvement. This does not mean directors need to approve every prompt. It means leadership sets the policy, assigns ownership, provides resources and reviews whether the system is working. Someone must be accountable for keeping the AI register current, responding to concerns and making sure controls are followed.

Supplier checks are central when you use third-party AI

Most SMEs will not train their own models. They will rely on external providers, which makes supplier management a major part of ISO 42001 implementation.

Before approving a tool, assess what it does with your information, whether it uses inputs to train its models, where data is processed, what security measures are available and how the supplier handles incidents. You should also consider service availability, contractual terms, intellectual property ownership and how easily the business could stop using the tool if needed.

A supplier’s popularity is not evidence that it is appropriate for every business use. Free consumer versions and paid business versions can have very different privacy, administration and retention settings. Your assessment should reflect the version your staff will actually use.

Keep records of the decision and review it when the supplier changes its terms, features or model. AI services develop quickly, so a one-off check at procurement stage is rarely enough.

ISO 42001 and other ISO standards

For many businesses, ISO 42001 will sit alongside existing management systems rather than operate alone. If you already work to ISO 9001, the ideas of documented processes, responsibilities, internal audits, corrective action and management review will be familiar. ISO 27001 provides a useful foundation where AI use involves confidential information, access controls and supplier security.

An integrated approach reduces duplication. The same document-control process can govern AI policies; the same internal audit programme can test AI controls; and the same management review can consider quality, information security and AI performance together. The key is to add AI-specific risks and objectives rather than copy another standard without adapting it.

This can be especially useful when a customer asks for evidence of responsible AI alongside quality or information-security assurances. Certification will not make an unsuitable AI use case safe, but it gives your organisation a credible structure for evaluating and managing it.

A practical route to ISO 42001 certification

The fastest route is usually to begin with a gap assessment against your current AI use. Identify the tools in play, decide your scope, assess the most material risks and set practical controls. From there, create the core AIMS documents, train relevant staff, gather evidence that the controls operate and carry out an internal review before certification assessment.

Do not over-engineer the system. An organisation with five employees and three approved tools needs a proportionate management system, not an enterprise governance department. Equally, avoid a paper-only exercise. Auditors will expect to see that your policies influence real decisions, including tool approval, staff behaviour, incident handling and management oversight.

A digital-first implementation can keep the workload manageable. ISO-Cert Online supports SMEs with customised templates, consultancy guidance and a central portal to organise documents, actions and progress without unnecessary site visits or disruption.

When ISO 42001 is worth prioritising

Certification is most compelling where AI affects customers, personal data, regulated activity, hiring, financial decisions or core service delivery. It can also strengthen tender responses where buyers want assurance that suppliers are adopting AI responsibly.

For lower-risk internal use, the business case may be more about getting ahead of unmanaged adoption. A clear AI management system lets you gain productivity benefits while protecting customer trust and avoiding avoidable mistakes. As AI becomes embedded in ordinary software, knowing what your organisation permits, monitors and reviews will become a practical business advantage.

Start with the AI tools your people are already using this week. A clear inventory, sensible approval rules and visible human accountability will give you a stronger foundation than waiting for every technology question to be answered.


Ready to get started?

Contact us today on +44 (0)333 014 7720 or email info@isocertonline.net for a free consultation. You can also get a quote online in minutes.

Don’t let cost hold you back from achieving ISO certification. With ISO-Cert Online, management systems certification is affordable for every business.

Posted on Google Google
Andrew Jackson profile picture
Andrew Jackson
4 September 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
I would like to provide the highest of recommendations to ISO-Cert Online Ltd. An extremely efficient and detailed service is provided and with all of the ISO Certifications which are required. The Integrated Management System that was provided to my Company is extremely thorough and already providing extremely great value and improvements to my Company. Their portal is also a great service to use currently and with regards to re-certification. I am greatly enjoying using the templates that were provided and they are extremely detailed. Claire and Steve are additionally extremely personable and highly responsive to any queries. ISO-Cert Online Ltd also provides great value for money and I am extremely glad that I chose to use their Company for ISO 9001 and 14001 certification.
Posted on Google Google
Tim Prestwood profile picture
Tim Prestwood
30 April 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Our experience with ISO-Cert Online has been exceptional. Completing our ISO 9001 and 14001 certifications felt like a daunting task at the start, but the team made the entire process straightforward and manageable for us at Virdis Chemicals. Steve and Claire are extremely professional and supportive partners. They consistently go out of their way to explain complex processes and identify clear areas where we can improve our systems. We truly appreciate their guidance and the clear roadmap they provided for our assessment. If you are looking for expert support with ISO certification, I cannot recommend them highly enough.
Posted on Google Google
Info MK Medicals UK profile picture
Info MK Medicals UK
12 February 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
ISO-Cert Online Ltd have been excellent to work with. Their team is consistently professional, responsive, and supportive, helping us keep our ISO certifications fully up to date with confidence. They are always available to assist, provide clear guidance, and maintain outstanding customer relations. A reliable and knowledgeable partner that we highly recommend. — MK Medicals (UK) Ltd
Posted on Google Google
Christian Hallam profile picture
Christian Hallam
3 February 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
After purchasing ISO 9001 & ISO 14001 certification for my company. Claire & Steve took the time to explain everything and support us through the process of creating and applying the new management system. Great value for money. ISO Cert Online helped to simplify what can be a complicated and confusing process. Thank you
Posted on Google Google
NIkos Xiros profile picture
NIkos Xiros
3 November 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Great company with excellent service. They’re always responsive, helpful, and ready to answer any questions you may have!
Posted on Google Google
Hannah Van-Der-Linden profile picture
Hannah Van-Der-Linden
24 June 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
We started looking at implementing ISO 9001 two years ago, and after numerous emails with Claire, we finally decided to embark on our ISO 9001 journey. We are now three months in and extremely grateful for the support and advice we've received. Steve has been instrumental in guiding us through the process. We’re looking forward to a long and successful working relationship with Steve and the team. - Greenway & Partners Ltd
Posted on Google Google
Aleks Dimitrova profile picture
Aleks Dimitrova
13 June 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
extremely quick and efficient, knowledgeable and responsive. Lovely Team, great company!
Posted on Google Google
Ali Madani profile picture
Ali Madani
5 November 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Steve's service was absolutely amazing, extremely fast turnaround, the save me a lot of hassle and time and they are so efficient that I couldn't recommend this company enough, I can only describe their service in one word FANTASTIC Thank you Steve and your team. Ali Madani EezzeE Ltd
Posted on Google Google
Elaine B profile picture
Elaine B
22 October 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Very professional service, easy to work with and delivered exactly what we asked for in the time frame quoted.
Posted on Google Google
Ged Riley profile picture
Ged Riley
18 October 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Great support on all things ISO
Article, Blog, News

7 Essential Steps to ISO 45001 Certification for Construction

Table of Contents

Why ISO 45001 Certification Matters for Construction Companies

Construction remains one of the highest-risk industries for workplace accidents and fatalities (the CDC). Without a structured approach to health and safety management, even small oversights can result in serious incidents, regulatory fines, and reputational damage. ISO 45001 certification provides a framework that transforms how organisations identify, assess, and control workplace hazards.

ISO 45001 is an internationally recognised standard that establishes a management system for occupational health and safety. It replaces the older OHSAS 18001 standard and aligns with the ISO management system family, making it easier for companies to integrate multiple certifications. For construction companies, this certification demonstrates to clients, suppliers, and regulators that health and safety is embedded into every operation.

Many construction businesses find that implementing ISO 45001 reduces accident rates, improves worker engagement, and strengthens their competitive position when bidding for contracts. Clients increasingly require ISO 45001 certification as a condition of supply chain participation, particularly for larger infrastructure and public sector projects.

At ISO-Cert Online, we work with construction firms to simplify their certification journey. Below, we’ll walk you through exactly how to achieve ISO 45001 certification for construction, from initial gap analysis through to certification.

Pro TipConstruction firms with 15-50 employees typically complete ISO 45001 implementation in 8-12 weeks when following a structured approach ([iso.org](https://www.iso.org/home/insights-news/resources/iso-45001-explained-what-it-is.html)). Remote assessment and digital documentation can accelerate this timeline significantly.

ISO 45001 Implementation Steps for Construction

Achieving full ISO 45001 certification for construction follows a logical seven-step process. Each phase builds on the previous one, creating a management system that works in practice, not just on paper.

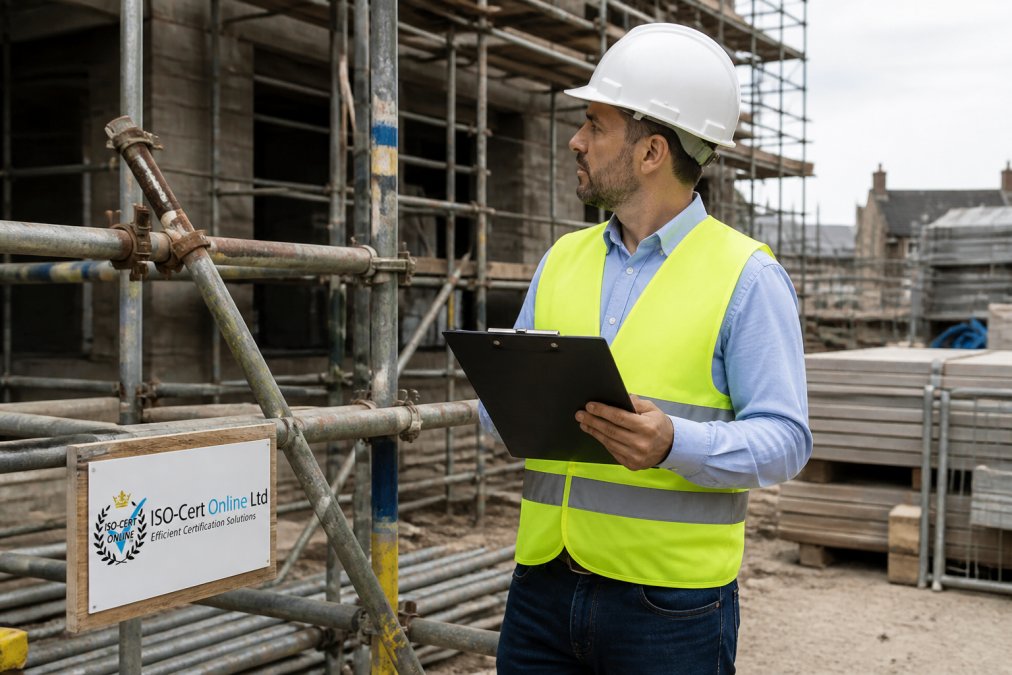
Construction workers in high-visibility gear reviewing safety documents for ISO 45001 certification for construction on site.

Step 1: Conduct a Gap Analysis

Before committing resources to implementation, you need to understand where your current health and safety practices stand relative to ISO 45001 requirements. A gap analysis compares your existing policies, procedures, and controls against the standard’s clauses.

This assessment examines your current health and safety policy, hazard identification and assessment processes, incident reporting and investigation procedures, worker training records, contractor management, and internal audit practices. The analysis identifies which elements already meet the standard and which require development or strengthening. Many construction firms discover they’re doing more than they realise; the gap is usually in documentation, consistency across sites, and evidence that demonstrates compliance.

Step 2: Develop Your Health and Safety Policy

Your health and safety policy is the foundation of your ISO 45001 certification for construction. This must reflect your organisation’s specific commitment to health and safety and set the direction for all management decisions.

The policy should include your commitment to comply with applicable legal requirements, prevent workplace injuries and ill health, and continually improve performance. It needs to define roles and responsibilities, establish how you’ll allocate resources, and explain how you’ll involve workers in health and safety decisions. Construction-specific policies must address site hazards: working at height, excavation safety, manual handling, noise exposure, and dust control. The policy should be signed by senior leadership to signal that health and safety is a board-level priority.

Step 3: Identify Hazards and Assess Risks

This step is where ISO 45001 certification for construction becomes operationally real. Hazard identification and risk assessment form the core of your management system. You’re systematically identifying what could cause harm and deciding what controls are needed.

For construction, this means evaluating hazards across all work activities: site setup, excavation, temporary works, working at height, manual handling, and equipment operation. You’ll consider hazards from plant and equipment, materials, environmental conditions, and work practices, including contractors and visitors on your sites. Risk assessment determines the likelihood and severity of harm, creating a prioritised list of control improvements needed before certification.

Step 4: Document Your Management System

Documentation is essential but should focus on what’s necessary and what’s used in practice. You’ll need documented procedures for hazard identification, risk assessment, incident investigation, contractor management, emergency response, and internal audit. Work instructions should exist for high-risk activities. Records include training logs, incident reports, audit findings, and management review notes.

The key is making documentation practical for site teams. Digital documentation platforms can simplify access and ensure site teams have current versions, improving compliance because information is accessible when needed.

Step 5: Train Your Workforce

Your workforce is essential to ISO 45001 certification for construction success. Workers must understand the health and safety policy, their responsibilities, and how to report hazards and incidents. Managers and supervisors need deeper training on their roles in implementing the management system.

Training should cover the ISO 45001 standard itself, your specific policies and procedures, hazard identification on your sites, and incident reporting. Induction training for new workers must include site-specific hazards and emergency procedures. Training needs to be ongoing as procedures evolve and new activities emerge.

Step 6: Conduct Internal Audits

Internal audits verify that your management system is working as documented. They’re about identifying where controls are breaking down so you can strengthen them before the external audit.

Internal audits should examine compliance with documented procedures, effectiveness of controls in reducing risks, and worker understanding of health and safety requirements. Auditors should include both management and worker representatives. For construction, audits should cover multiple sites to ensure consistency. Most construction firms conduct internal audits quarterly, with findings documented and corrective actions tracked to completion.

Step 7: Prepare for External Certification Audit

The external auditor will review your documented system and examine records remotely. They’re verifying that your management system is documented, implemented, and effective.

Preparation involves ensuring documentation is complete and accessible, confirming corrective actions from internal audits and management review meetings are being addressed.


ISO 45001 Implementation Timeline for Construction

The timeline for ISO 45001 implementation for construction varies based on your current health and safety maturity and organisational size.

Initial gap analysis and planning typically takes 2-3 weeks. Policy development and hazard identification usually require 4-6 weeks. Documentation development and workforce training span 6-8 weeks. Internal audits and corrective actions take 4-6 weeks.

From start to full certification, construction firms typically complete the process in 4-5 months. Some organisations with strong existing health and safety practices complete it faster. Others with multiple sites or complex operations may require longer.

Key TakeawayMost construction SMEs achieve full ISO 45001 certification within 12-16 weeks when following a structured implementation plan and allocating adequate resources to the process.

CDM 2015 and ISO 45001 Alignment

The Construction (Design and Management) Regulations 2015 (CDM 2015) establish legal duties for health and safety on construction projects (hse.gov.uk). ISO 45001 certification for construction complements CDM 2015 compliance by providing a systematic management framework.

CDM 2015 requires duty holders to manage health and safety throughout a project. ISO 45001 provides the organisational systems to fulfil these duties consistently. For example, CDM 2015 requires hazard identification and risk assessment; ISO 45001 provides the documented process for doing this systematically across all projects.

Many construction firms find that implementing ISO 45001 strengthens their CDM 2015 compliance. The standard’s requirements for contractor management align with CDM duties to coordinate and communicate with supply chain partners. The incident investigation and management review processes support the continuous improvement that CDM expects.

ISO 45001 is broader than CDM 2015, applying to all construction work and covering occupational health risks beyond construction-specific hazards. CDM 2015 compliance is a legal minimum; ISO 45001 certification demonstrates a more comprehensive commitment to health and safety management.


ISO 45001 Audit Checklist for Construction

The external certification audit assesses your management system against ISO 45001 requirements. Understanding what auditors examine helps you prepare effectively.

Safety auditor checking site equipment for ISO 45001 certification for construction during a formal compliance inspection.

Organisational Context and Leadership. Auditors verify that senior leadership understands the health and safety context, has committed resources to the management system, and can demonstrate involvement. They’ll review your health and safety policy and confirm it’s communicated throughout the organisation.

Planning and Hazard Management. The audit examines how you’ve identified hazards, assessed risks, and determined necessary controls. Auditors will verify that hazard identification is comprehensive, risk assessments are documented, and controls are appropriate for construction-specific hazards and contractor management.

Support and Competence. Auditors confirm that you’ve allocated resources, provided training, and established competence requirements. They’ll review training records and verify that contractors meet your competence standards.

Operational Control. This examines how you control high-risk activities. Auditors review work procedures, and verify that controls are actually implemented. They’ll check incident reporting systems, emergency procedures, and contractor supervision.

Performance Evaluation. Auditors review your internal audit programme, management review process, and how you monitor health and safety performance. They’ll examine incident records, audit findings, and corrective actions to verify you’re identifying and addressing problems.

Improvement and Continual Development. The audit confirms that you’re learning from incidents and audit findings, implementing corrective actions, and continually improving your management system.

Audit Area

What Auditors Examine

Common Construction Issues

Health and Safety Policy

Leadership commitment and communication

Policy too generic or not site-specific

Hazard Identification

Completeness and documentation

Missing site-specific hazards or contractor risks

Risk Assessment

Appropriateness of controls

Insufficient controls for high-risk activities

Training Records

Competence and understanding

Inadequate induction or refresher training

Incident Management

Investigation and corrective action

Incomplete incident records or weak investigations

Contractor Management

Competence verification and supervision

Inadequate contractor vetting or oversight


Tools and Support to Simplify Your Certification Journey

Several tools and resources can simplify ISO 45001 certification for construction. The right support depends on your current maturity, available resources, and timeline.

Compliance Software Platforms. Organisations like Zebsoft and BuiltRight Technologies offer software specifically designed for construction health and safety management. These platforms centralise hazard registers, incident reporting, training records, and audit management. For construction firms managing multiple sites, integrated software reduces the documentation burden and ensures consistency.

Workforce Competency Management. Competency Cloud specialises in tracking worker certifications and training records, essential for construction where many roles require specific qualifications. The platform maintains audit-ready evidence of worker competence.

Consultancy Support. Other providers offer end-to-end implementation support. Consultants guide your gap analysis, help develop documentation, train your team, and prepare you for the external audit. This approach is particularly valuable if your team lacks health and safety expertise or if you’re managing multiple sites.

ISO-Cert Online Ltd offers remote assessment and digital documentation approaches that simplify the certification process. Remote assessments work effectively for construction firms because auditors can assess your documented system and site practices without requiring extensive on-site time.

Best ForConstruction SMEs with 15-50 employees seeking cost-effective certification typically benefit from compliance software combined with targeted consultancy support for gap analysis and audit preparation.

Conclusion

ISO 45001 certification for construction is increasingly essential for competing in the modern construction market. Clients require it for tender participation, supply chain partners expect it, and it demonstrates genuine commitment to worker safety.

The seven-step implementation process provides a clear pathway. Construction firms typically complete implementation within 4-5 months when they allocate adequate resources and follow a structured approach.

The real value extends beyond the certificate. Organisations that genuinely implement ISO 45001 see reduced incident rates, improved worker engagement, and stronger operational discipline. The management system becomes part of how you work, not a compliance burden.

ISO Certification Online supports construction firms through remote assessments and digital documentation, making certification faster and more efficient. With flexible approaches designed for SMEs, the path to ISO 45001 certification for construction has become significantly more accessible.

Frequently Asked Questions

Is ISO 45001 mandatory for construction companies?

ISO 45001 is not legally mandatory in the UK, but many construction clients require it as a condition of contract. Organisations working on major projects, particularly those governed by CDM 2015 regulations, often need certification to bid successfully. Additionally, insurance providers and supply chain partners frequently demand ISO 45001 as proof of a robust occupational health and safety management system. Achieving certification demonstrates your commitment to protecting workers and managing workplace risks systematically.

How long does ISO 45001 certification typically take?

The timeline varies depending on your starting point and company size. Most construction businesses complete implementation within 2-6 months, though some take longer if significant changes to existing systems are needed. The process includes gap analysis, documentation development, staff training, internal audits, and the final external certification audit. Remote assessment options can accelerate timelines by reducing scheduling delays associated with on-site visits, allowing your team to progress documentation and training while audit scheduling is arranged.

How does ISO 45001 align with CDM 2015 requirements?

ISO 45001 provides the management framework to fulfil many CDM 2015 obligations. Both standards require hazard identification, risk assessment, worker competence management, incident investigation, and documented procedures. ISO 45001 helps construction companies demonstrate systematic control of health and safety risks, which supports CDM 2015 compliance for duty holders. However, CDM 2015 imposes additional specific requirements around project notification, coordination, and health and safety file management that sit outside ISO 45001’s scope, so organisations must address both frameworks comprehensively.

What should be included in an ISO 45001 audit checklist for construction?

A construction-specific audit checklist should verify: hazard identification and risk assessment for your site operations; documented procedures for high-risk activities such as working at height, manual handling, and machinery operation; evidence of worker competence and training records; incident and near-miss reporting systems with investigation records; personal protective equipment provision and inspection; site induction and toolbox talk documentation; contractor management and site safety rules; emergency procedures and first aid provision; and management review minutes demonstrating leadership commitment. The checklist should also confirm that your system addresses project-specific risks and aligns with CDM 2015 requirements where applicable.

Will remote assessment work for ISO 45001 certification in construction?

Yes, remote assessment can work effectively for construction companies. The auditor will conduct interviews with your management and workforce via video, review your documented system and evidence digitally, and request photographs or video walkthroughs of your site and facilities. This approach works well for smaller sites and offices. However, for larger, complex operations across multiple locations, a hybrid model combining remote document review with limited on-site visits may provide more thorough verification. The key is ensuring your documentation, evidence, and worker testimony clearly demonstrate system compliance without requiring the auditor to be physically present.


Now, are you ready to get started with ISO 45001 Certification for Construction?

Contact us today on +44 (0)333 014 7720 for a free consultation regarding ISO 45001 Certification for Construction. Additionally, you can also get a quote online in minutes.

Don’t let cost hold you back from achieving ISO certification. With ISO-Cert Online, management systems certification is affordable for every business.

Posted on Google Google
Andrew Jackson profile picture
Andrew Jackson
4 September 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
I would like to provide the highest of recommendations to ISO-Cert Online Ltd. An extremely efficient and detailed service is provided and with all of the ISO Certifications which are required. The Integrated Management System that was provided to my Company is extremely thorough and already providing extremely great value and improvements to my Company. Their portal is also a great service to use currently and with regards to re-certification. I am greatly enjoying using the templates that were provided and they are extremely detailed. Claire and Steve are additionally extremely personable and highly responsive to any queries. ISO-Cert Online Ltd also provides great value for money and I am extremely glad that I chose to use their Company for ISO 9001 and 14001 certification.
Posted on Google Google
Tim Prestwood profile picture
Tim Prestwood
30 April 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Our experience with ISO-Cert Online has been exceptional. Completing our ISO 9001 and 14001 certifications felt like a daunting task at the start, but the team made the entire process straightforward and manageable for us at Virdis Chemicals. Steve and Claire are extremely professional and supportive partners. They consistently go out of their way to explain complex processes and identify clear areas where we can improve our systems. We truly appreciate their guidance and the clear roadmap they provided for our assessment. If you are looking for expert support with ISO certification, I cannot recommend them highly enough.
Posted on Google Google
Info MK Medicals UK profile picture
Info MK Medicals UK
12 February 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
ISO-Cert Online Ltd have been excellent to work with. Their team is consistently professional, responsive, and supportive, helping us keep our ISO certifications fully up to date with confidence. They are always available to assist, provide clear guidance, and maintain outstanding customer relations. A reliable and knowledgeable partner that we highly recommend. — MK Medicals (UK) Ltd
Posted on Google Google
Christian Hallam profile picture
Christian Hallam
3 February 2026
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
After purchasing ISO 9001 & ISO 14001 certification for my company. Claire & Steve took the time to explain everything and support us through the process of creating and applying the new management system. Great value for money. ISO Cert Online helped to simplify what can be a complicated and confusing process. Thank you
Posted on Google Google
NIkos Xiros profile picture
NIkos Xiros
3 November 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Great company with excellent service. They’re always responsive, helpful, and ready to answer any questions you may have!
Posted on Google Google
Hannah Van-Der-Linden profile picture
Hannah Van-Der-Linden
24 June 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
We started looking at implementing ISO 9001 two years ago, and after numerous emails with Claire, we finally decided to embark on our ISO 9001 journey. We are now three months in and extremely grateful for the support and advice we've received. Steve has been instrumental in guiding us through the process. We’re looking forward to a long and successful working relationship with Steve and the team. - Greenway & Partners Ltd
Posted on Google Google
Aleks Dimitrova profile picture
Aleks Dimitrova
13 June 2025
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
extremely quick and efficient, knowledgeable and responsive. Lovely Team, great company!
Posted on Google Google
Ali Madani profile picture
Ali Madani
5 November 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Steve's service was absolutely amazing, extremely fast turnaround, the save me a lot of hassle and time and they are so efficient that I couldn't recommend this company enough, I can only describe their service in one word FANTASTIC Thank you Steve and your team. Ali Madani EezzeE Ltd
Posted on Google Google
Elaine B profile picture
Elaine B
22 October 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Very professional service, easy to work with and delivered exactly what we asked for in the time frame quoted.
Posted on Google Google
Ged Riley profile picture
Ged Riley
18 October 2024
Google star 1Google star 2Google star 3Google star 4Google star 5Trustindex verifies that the original source of the review is Google.
Great support on all things ISO
Blog, News

Online vs Traditional ISO Certification: What’s the Real Difference?

Picture this: you’ve spent weeks polishing a tender response for a massive buyer. Everything looks tight until you hit page six.

There it is: a strict requirement for an ISO 9001 quality mark. No exceptions. Deadline? Next Friday.

The traditional path feels hopeless right out of the gate. You’re looking at weeks of back-and-forth emails, thousands in consultant fees, and an auditor trailing your staff around the office with a clipboard.

Then you run into confusion: online ISO certification vs traditional certification.

Online ISO certification sounds almost too smooth: digital uploads, video interviews, fast turnaround, zero travel costs. But then that nagging doubt kicks in: If nobody actually steps foot in my building, does the certificate even hold up in the real world?

The short answer? Yes, 100%.

An online ISO certificate carries the exact same weight, validity, and commercial status as one earned through on-site visits, provided it comes from an accredited certification body. The difference isn’t what gets checked or how high the bar is set; it’s simply how the evidence moves from your hands to the auditor’s desk.

What “online ISO certification” actually means

Let’s clear up a massive misconception straight away. Online certification isn’t a “diet” version of the standard, nor is it a legal loophole.

If your business goes after ISO 9001 (Quality), ISO 14001 (Environmental), ISO 45001 (Occupational Health & Safety), ISO 27001 (Information Security), or any other ISO standard online, you have to satisfy every single clause of the exact same international standard as a global enterprise being audited in person.

The difference comes down to the tools being used. Instead of paying an assessor to spend three hours in traffic only to sit in your conference room reading paper binders, the process uses modern digital auditing tools:

  • Document evidence portals: Policies, logs, and processes get uploaded directly to cloud compliance hubs (like the ISO-Cert Unite™ portal).
  • Remote assessments & desktop audits: Auditors may evaluate files on screen, conduct interviews over video links, and review digital records.

This whole setup operates under strict rules. Legitimate certification bodies comply with ISO 17021, the international standard governing how audit bodies behave and answer to national oversight bodies in the UK. Whether an auditor looks at your records over a desk or over Zoom, their corporate obligations don’t change.

How a remote audit actually works, step by step

Never done a remote audit? It’s surprisingly simple, stripped of the usual on-site drama.

  1. Document Upload & Initial Setup: You upload your tailored management system documents, risk assessments, and proof of implementation into a secure cloud system.
  2. Desktop Audit & Portal Review: The auditor completes a Stage 1 review, checking your written setup remotely to ensure every required clause is covered.
  3. Evidence Sampling: The auditor picks random records, such as a recent customer complaint log, training registers, or internal audit notes, to confirm daily routines actually match what’s on paper.
  4. Certification Decision: Any non-conformance gets flagged for a quick fix. Once signed off, the formal certificate is issued.

What stays exactly the same as traditional certification

Comparing online ISO certification vs traditional certification side-by-side reveals that the core work doesn’t change at all. You skip the travel invoices and empty tea-making etiquette, not the compliance rigour.

  • Same ISO Requirements: Annex SL structure, continuous improvement, risk-based thinking it all applies.
  • Same Oversight: Audit rules remain tied to international accreditation standards.
  • Same Surveillance Cycle: You still go through annual surveillance audits across the standard 3-year certification cycle.
  • Same Physical Certificate: Your issued certificate shows your scope, accreditation marks, and company name.


Where online certification is a genuinely better fit

While both routes yield valid compliance, remote processes make far more sense for the way modern companies operate.

Desk-Based and Single-Site Businesses

If your team spends 90% of their day behind screens, as IT support, recruitment agencies, digital marketers, or consultancies, having an auditor physically present adds almost zero assessment value. A remote ISO audit verifies your digital assets and workflows right where they live.

Busy SME Owners

For a small company, hosting an assessor for two solid days means pulling key people away from actual revenue-producing work. Uploading evidence digitally lets you work through compliance checks on your own clock.

Urgent Tender Deadlines

Need ISO certification without a site visit to hit a tender cutoff? On-site audits suffer from scheduling gridlock; assessors are often unavailable for months. Digital workflows eliminate travel overhead, cutting turnaround down to a matter of days.

Where a traditional/on-site audit still makes more sense

Remote auditing isn’t a magic wand for every industry on the planet.

Complex Manufacturing & Heavy Industry

If you run a chemical plant, a steel workshop, or a busy production line, physical walkthroughs can be valuable. An auditor may want to see material flows, observe floor safety habits, and inspect physical machinery up close. A remote audit can still be useful in checking these things however, by focusing on the specifics involved, e.g. robust risk assessments and records of preventive actions that have been implemented, as well as corrective and follow-up actions carried out.

High-Hazard Health & Safety

For the purposes of a remote audit, ISO 45001 certification for health and safety in high-hazard areas such as construction sites or demolition projects, desk review may not be adequate. The assessment of physical risk factors, personal protective equipment usage, and control of access to the site generally benefits from the auditor being on-site.

Rule of thumb: If your risks are contained within the physical equipment and hazardous environment, then you should invest in the on-site visit. If your risks are contained within information or software, or service delivery, then go remote.

Is online ISO certification actually legitimate?

The bottom line: Yes, online ISO certification is completely legitimate. Legitimacy comes down to accreditation, not where the auditor sits.

A common worry among Directors is that a prospective client might turn down a certificate earned remotely. But here’s the reality: procurement officers never ask, “Did the auditor physically drive to your office?” They ask, “Is this certificate backed by a recognised accreditation body?”

Frequently Asked Questions

1. Is an online ISO certificate the same as one from an on-site audit?

Yes, totally identical. Both methods evaluate the same standards, use the same accreditation rules, and yield the exact same certificate. No client or tender board can tell or care how the audit evidence was collected.

2. Do auditors ever visit in person for online certification?

Not usually for office-based or low-risk setups. However, if your business scope involves complex physical hazards or an unexpected gap turns up during desktop review, a targeted physical visit might be requested.

3. Which ISO standards can be certified remotely?

Most management frameworks work great remotely, especially ISO 9001 (Quality), ISO 14001 (Environmental), ISO 27001 (Information Security), ISO 22301 (Business Continuity), and ISO 45001 (Health & Safety for low-risk environments).

4. How long does online ISO certification take compared to traditional?

Traditional on-site routes take anywhere from 3 to 9 months because of calendar conflicts, travel plans, and paperwork delays. Modern digital portals like ISO-Cert Unite™ compress that timeframe, letting prepared SMEs finish the whole cycle in days.

Streamline Your ISO Compliance Today

Getting your business certified shouldn’t mean drowning in paper, waiting months for audit dates, or losing days of productivity. If you need ISO 9001, ISO 14001, or an integrated management system for an upcoming tender, modern online assessments get you there fast without the stress.

Want to see how straightforward it can be? Get an instant quote or check out how our ISO-Cert Unite™ portal cuts the hassle out of compliance.

Privacy Settings
We use cookies to enhance your experience while using our website. If you are using our Services via a browser you can restrict, block or remove cookies through your web browser settings. We also use content and scripts from third parties that may use tracking technologies. You can selectively provide your consent below to allow such third party embeds. For complete information about the cookies we use, data we collect and how we process them, please check our Privacy Policy
Youtube
Consent to display content from - Youtube
Vimeo
Consent to display content from - Vimeo
Google Maps
Consent to display content from - Google
Spotify
Consent to display content from - Spotify
Sound Cloud
Consent to display content from - Sound