Articles Tagged with

The year 2025 is a significant year for ISO certification, as two of the most widely used ISO standards are set to be updated after nearly a decade of waiting.…

The year 2025 is a significant year for ISO certification, as two of the most widely used ISO standards are set to be updated after nearly a decade of waiting.…
Managing multiple ISO standards separately can be cumbersome. Separate manuals, overlapping procedures and multiple audits eat up time and resources. An integrated management system (IMS) simplifies this complexity by combining the requirements of different standards into a single framework. For growing businesses seeking efficiency and a competitive edge, integrating standards is becoming the norm.
ISO standards share many common elements: the Plan‑Do‑Check‑Act cycle, leadership commitment, risk‑based thinking and documented information requirements. When organisations maintain separate systems for quality, environment, health and safety or information security, they often duplicate processes and policies. For example, one department might conduct a risk assessment for ISO 9001 while another performs a similar exercise for ISO 14001. An IMS aligns these activities, eliminating redundancy and allowing resources to be focused on improvement rather than administration.
Combining ISO 9001 (quality), ISO 14001 (environment) and ISO 45001 (health and safety) yields powerful synergies. Quality and environmental objectives often overlap; reducing defects, for instance, cuts waste and energy use. Health and safety initiatives improve workforce morale, which in turn leads to higher quality products. Integrating ISO 27001 (information security) or ISO 22301 (business continuity) further strengthens resilience by ensuring that processes remain secure and operational during disruptions. An integrated system makes it easier to manage these interdependencies because objectives, resources and responsibilities are aligned.
The primary benefit of an IMS is efficiency. With a unified manual, businesses reduce the amount of documentation they need to create and maintain. Audits can be combined, saving time and reducing disruption. Training becomes simpler, as staff learn one system rather than several. Decision‑making improves when information flows through a single system – managers can see how a change in one area affects other parts of the business. A coherent management system also presents a consistent message to customers and regulators, reinforcing the organisation’s commitment to quality, sustainability and safety.
Cost savings are another significant advantage. By eliminating duplicate processes and consolidating audits, an IMS reduces administrative overhead. Certification bodies often offer discounted audit rates for integrated systems because auditors can cover multiple standards in a single visit. Internally, teams spend less time preparing for separate audits and more time working on improvements that drive value.
After certification, the focus shifts to continual improvement. Use management reviews to assess performance across all standards, identify trends and set new objectives. Encourage employees to suggest improvements and report issues. Monitor regulatory changes; for example, if new environmental legislation emerges, update your system accordingly. Keep an eye on emerging standards like ISO 50001 (energy management) or ISO/IEC 42001 (AI governance), which may become relevant as your business evolves.
An integrated management system supports growth by providing a scalable framework. When entering new markets, adding products or acquiring other companies, an IMS allows you to incorporate new activities without reinventing your management systems. Integrated systems can also improve customer trust and market access; many clients prefer working with suppliers who hold multiple certifications because it reduces risk. Additionally, integrated systems provide better data for decision‑making, enabling leaders to balance quality, sustainability and safety considerations effectively.
As markets demand greater transparency and responsibility, integrated management systems will become increasingly common. Organisations that combine standards not only streamline compliance but also demonstrate maturity and foresight. Trends such as climate‑related disclosure, heightened cyber threats and emerging AI regulation will favour businesses with flexible, holistic management systems. By embracing integration now, you create a robust foundation for innovation, resilience and sustainable growth.
Find out more…
If you would like to find out more about ISO standards, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
Digital transformation is reshaping nearly every aspect of business, including the way organisations achieve and maintain ISO certification. Paper‑based documents, manual audits and in‑person meetings are giving way to cloud portals, remote assessments and even artificial intelligence. For small and medium enterprises looking to certify quickly and efficiently, embracing these technological tools isn’t a luxury – it’s a necessity.
Historically, certification meant lengthy on‑site audits, boxes of paperwork and waiting for physical signatures. Today, software platforms manage documents and evidence, auditors review files via secure portals and sign‑offs happen electronically. Digital certification reduces travel time, shortens approval cycles and makes it easier for geographically dispersed teams to collaborate. In the wake of the pandemic, many accreditation bodies have formalised remote auditing procedures, providing clear guidelines for video conferencing, screen sharing and secure file transfer. This has opened ISO certification to businesses in rural areas or overseas markets who previously struggled with travel logistics.
A robust document management system is the backbone of a modern ISO programme. Templates, policies, procedures and records must be controlled, versioned and easily accessible. Cloud‑based platforms like SharePoint or specialised ISO management software allow teams to collaborate in real time, assign tasks and track progress. They also enable remote auditors to access documentation without the need for endless email chains. When choosing a platform, look for features such as user permissions, audit trails, encryption at rest and in transit, and integration with common productivity suites. These features not only simplify certification but also help meet ISO 27001 requirements for protecting information.
The next frontier in ISO certification involves artificial intelligence (AI). AI doesn’t replace human judgement, but it can automate routine tasks and highlight areas of concern. For instance, natural language processing can analyse policies and identify clauses that deviate from standard requirements. Machine learning algorithms can review incident logs or non‑conformity reports to detect patterns and predict future risks. Chatbots integrated into your portal can answer basic questions from staff about procedures or explain the purpose of a particular form. Implemented thoughtfully, AI reduces the administrative burden on quality managers and auditors, freeing them to focus on strategic improvements.
With the rise of AI, the International Organisation for Standardisation and the International Electrotechnical Commission introduced ISO/IEC 42001, the first management system standard for artificial intelligence. It provides a framework for organisations to responsibly govern AI systems, ensuring transparency, accountability and alignment with ethical principles. For businesses already certified to ISO 9001 or ISO 27001, adopting ISO/IEC 42001 can slot into existing structures, particularly if they use an integrated management system. The standard covers topics such as data quality, algorithm bias, human oversight and continual improvement – areas that will become increasingly important as AI permeates supply chains and service delivery.
Remote audits require more planning than on‑site visits. Before the audit, ensure that all documents are uploaded to your portal and correctly named. Check that your video conferencing tools are working and that everyone knows how to share screens. During the audit, maintain open communication with the assessor. Use a headset with a quality microphone to avoid miscommunications, and prepare to demonstrate processes live using webcams or recorded footage. After the audit, record lessons learned to streamline the next one. Many organisations report that remote audits are less disruptive to business operations and reduce the environmental impact associated with travel.
Training is a core requirement of many ISO standards, and technology has transformed how it’s delivered. Interactive online courses, virtual classrooms and micro‑learning modules allow employees to learn at their own pace. They also make it easier to schedule training around busy workloads. Digital training platforms often include knowledge checks, certificates of completion and integration with HR systems to keep records up to date. When employees can access training materials on demand, they are more likely to retain knowledge and apply it to their work, strengthening your management system.
With digital tools come new responsibilities. Storing and transmitting sensitive documents requires strong security controls. Encryption, multi‑factor authentication, and regular vulnerability assessments are essential. Organisations seeking ISO 27001 certification should ensure that their chosen platforms comply with the standard’s Annex A controls. Data protection laws like the General Data Protection Regulation (GDPR) in Europe also impose strict requirements on how personal data is collected and processed. By choosing vendors that prioritise security and privacy, you not only protect your business but also build trust with customers and auditors.
No single tool will meet every organisation’s needs. Start by mapping your current processes and identifying pain points – perhaps version control is a headache, or you struggle to schedule training. Research solutions that address those specific issues and ask vendors about integration capabilities. Consider scalability: will the platform support additional standards like ISO 45001 or ISO 22301 as your management system evolves? Evaluate the vendor’s support model, as responsive support is vital when issues arise during an audit. Finally, involve your team in the selection process to ensure that the solution is user‑friendly and aligns with company culture.
Technology will continue to shape how organisations achieve and maintain certification. Advances in AI, blockchain for secure record keeping, and virtual or augmented reality for training and process demonstration are already on the horizon. By embracing digital tools today, you set your organisation up for agility and resilience. Remote audits, automated document management and AI‑driven insights streamline compliance, reduce costs and free up time for innovation. In the coming years, businesses that adopt technology as part of their ISO journey will not only meet regulatory requirements but also gain a competitive edge.
Find out more…
If you would like to find out more about ISO standards, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
The team here at ISO-Cert are proud to announce the launch of our brand-new online management systems portal, ISO-Cert UniteTM, which has been designed with the aim of helping to make ISO certification as stress-free and efficient as possible.
This is the only online portal in the industry that will guide you through every step of the implementation process from start to finish, with appropriate tasks set each month to ensure that you stay on track and hit the pre-defined targets.
We also automatically monitor your progress 24/7 so you can catch any problems early on, enabling you to take action immediately to prevent potential delays. Flexibility and versatility are also assured, as the portal can be used for any ISO management system standard.
If you’re looking for globally recognised ISO certification delivered efficiently and cost effectively, the ISO-Cert team can help you every step of the way.
As well as our industry-first online portal, we also offer management systems consultancy and training, designed to help you take your business to the next level.
Find out more…
If you would like to find out more about the ISO-Cert UniteTM portal, how your business could benefit from implementing a Management System, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
Digital health technology is becoming increasingly commonplace, helping to transform patient care pathways, boosting health and wellbeing, making health systems more efficient, delivering cost savings and empowering people to manage their own conditions more successfully.
Virtual care is capable of reaching significantly more people than in-person appointments, but there are some concerns about healthcare digitisation, particularly from the perspective of businesses operating in this sector, which demands consistent service delivery and proactive risk management.
Digital health solutions of all kinds, including the likes of software as medical devices, artificial intelligence as medical devices, 3D printing, mobile apps, virtual assistants, wearable medical devices, robotics and virtual care provision, must remain compliant with all relevant regulations and standards, including DCB 0129, the Data Security and Protection toolkit and Digital Technology Assessment Criteria.
These standards (among others) serve to ensure that products, processes and systems are secure, robust, accessible and clinically safe – but it’s important to note that they don’t cover complete organisational structures, so it may be beneficial to investigate ISO 9001 certification as well.
The ISO 9001 standard is currently undergoing major amendments (having been left unchanged for ten years or so), with the expected updates now delayed until September 2026… so it’s perhaps fair to say that they’re likely to be quite significant.
As such, now’s the perfect time to prepare for potential changes and it’s likely that there will be even greater focus placed on digital transformation.
This particular standard isn’t industry-specific, but it is highly relevant to those businesses working in digital health. Certification will ensure that your organisation has a clear framework in place to deliver your products and services consistently, and efficiently, as well as driving improvements as appropriate over time.
You’ll also find that your approach to risk management is properly supported, improving both the patient experience and your organisation’s activities, and making sure that your business is able to maintain this as you grow and thrive.
If you’re involved in the design, production and servicing of medical devices, you’ll need to consider ISO 13485 certification to ensure patient safety and compliance with regulations.
This would be a good option if you’re keen to tick all the ISO 9001 boxes but want to be particularly vigilant and ensure compliance as your products and services develop.
As digital health technologies continue to emerge, with key innovations including the likes of mobile health apps, connected wearable devices, digitised health systems, patient data and prescription delivery, telemedicine, health data analytics, personalised medicine and both AI and machine learning (ML), regulations are certain to evolve to ensure that safety, quality and performance standards continue to be met.
Key areas of focus include data protection and privacy, ensuring compliance with GDPR by safeguarding patient data. Medical device regulation (prioritising safety, quality and performance of tech), telemedicine and remote care, and clinical safety and effectiveness continue to be of particular importance for businesses.
Finally, cybersecurity is another area of focus that companies would be wise to put at the top of the agenda, making sure that health data is secure and the appropriate levels of protection against cyber attacks are implemented.
Find out more…
If you’d like to find out more about the evolving digital health landscape and what you can do to prepare for regulatory changes, please contact us on 0333 014 7720 or email info@isocertonline.net.
The National Cyber Security Centre’s (NCSC’s) eighth annual review was published at the end of last year, detailing the major cyber security threats and trends facing the UK, as well as predicting what challenges will lie ahead in the future… with the 2024 cyber threat landscape described as both diffuse and dangerous.
It was found that cyber incidents are becoming increasingly frequent and their impact increasingly severe, with ransomware identified as being the most pervasive cyber threat to organisations.
Use of artificial intelligence (AI) is also increasingly being seen, driving up the volume and heightening the impact of these attacks.
For the 2023/2024 year, 430 incidents were handled by the NCSC (up from the 371 seen the year before), with the main sectors reporting ransomware activity emerging as legal, IT, manufacturing, academia, construction, and charities.
Commenting ahead of the review publication, new CEO of the NCSC Richard Horne said: “What has struck me more forcefully than anything else since taking the helm at the NCSC is the clearly widening gap between the exposure and threat we face, and the defences that are in place to protect us.
“And what is equally clear to me is that we all need to increase the pace we are working at to keep ahead of our adversaries.
“The NCSC, as the National Technical Authority, has been publishing advice, guidance, and frameworks since our inception, in a bid to drive up the cyber security of the UK. The reality is that advice, that guidance, those frameworks need to be put into practice much more across the board.
“We need all organisations, public and private, to see cyber security as both an essential foundation for their operations and a driver for growth. To view cyber security not just as a ‘necessary evil’ or compliance function, but as a business investment, a catalyst for innovation and an integral part of achieving their purpose.”
Aside from ransomware, other cyber-attacks to be on your guard against include malware, phishing, spoofing, code injections, social engineering, denial of service, tunnelling and – increasingly – both Internet of Things and AI-powered incidents.
The risks to businesses across all industries and sectors are very real and the consequences can be catastrophic.
This means that organisations must make sure they invest in innovative cyber security strategies to prevent attacks and ensure that they can recover quickly if the worst does happen, building resilience into systems, processes, and procedures to mitigate the effects.
Being more cyber resilient means that you’ll be better able to withstand and recover from a wide range of different attacks, identifying ways in which you can minimise the impact so that your business can continue to operate no matter what.
Your cyber security strategy should include:
– Preventative and detective measures
– Corrective controls
– General disaster recovery and continuity plans
– How you intend to continue operating in the event of an attack
– The strategies you’ll use to recover your data and systems
– Risk management processes where you identify, assess and mitigate incidents.
Also make sure that you focus on supply chain security when putting these strategies together, so you know that your suppliers and third-party vendors are also secure and won’t put your systems at risk.
And, finally, you also need to carry out awareness campaigns within the office environment itself so that your employees, from top to bottom, know what their responsibilities are, know what to look out for and know what to be on their guard against.
By embracing both the concept of cyber security and cyber resilience, you’ll naturally find that other aspects of your business improve at the same time.
You’ll develop a deeper understanding of your organisation, identifying what’s most critical to your operations and what your inherent strengths and weaknesses are, enabling you to deliver wholesale organisational change – and to evolve over time in line with future developments, both internally and externally.
Just today (April 8th), the government has published new guidance to help directors and company boards shore up cyber defences to further protect organisations from the growing prevalence of online threats.
The new Code of Practice details how daily operations can be protected, including having a cyber strategy in place to ensure that risk management supports resilience and growth effectively, as well as promoting a cyber secure culture within your organisation and implementing incident response plans.
Figures show that 74 percent of large businesses and 70 percent of medium-sized companies have experienced breaches and attacks in the last 12 months, with these threats costing the UK economy nearly £22 billion annually between 2015 and 2019 and having significant impacts on company operations and reputations.
Despite this, one-third of large businesses still don’t have a formal cyber strategy in place, while almost 50 percent of medium-sized companies don’t have an incident response plan backing them up.
One of the best ways to enhance your credibility, improve operational efficiencies and risk management procedures, as well as increasing customer confidence and demonstrating your commitment to business continuity and continual improvement is to consider ISO certification.
There are two ISO standards that lend themselves neatly to addressing cyber-crime: ISO 27001 for information security (the prevention standard), and ISO 22301 for business continuity (the impact minimisation standard).
ISO 27001 supports businesses in ensuring that their security systems are robust and up to date to prevent data breaches, with certification guiding you on how to set up, implement, maintain, and continually improve information security management systems.
ISO 22301:2019 will provide the framework for your business for minimising the impacts against unexpected events, everything from cyber-attacks and natural disasters to pandemics and supply chain disruption.
Find out more…
If you would like to find out more about cyber security standards and making your business more resilient, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.

In today’s fast-paced digital world, businesses are increasingly turning to artificial intelligence (AI) to enhance operations and drive innovation. However, with great power comes great responsibility, and the new ISO standard for AI is designed to ensure ethical AI implementation across the board.
This comprehensive AI management framework emphasises transparency in AI processes, accountability in AI systems, and adherence to AI guidelines that foster trust in AI technologies. For companies eager to stay competitive and build credibility, understanding and adopting these standards is not just beneficial—it’s essential.
The ISO Standard for AI represents a significant milestone in the development and deployment of artificial intelligence technologies. This section explores the fundamentals of ethical AI implementation, the importance of a robust AI management framework, and how these standards contribute to building trust in AI technologies.
Ethical AI implementation forms the cornerstone of responsible technology development. It ensures that AI systems are designed and deployed with consideration for human values, fairness, and societal impact.
The ISO standard for AI provides a comprehensive framework for organisations to navigate the complex ethical landscape of AI. This includes guidelines on data privacy, algorithmic bias mitigation, and transparency in decision-making processes.
By adhering to these standards, businesses can create AI systems that not only perform efficiently but also align with ethical principles and societal expectations.
An AI management framework is crucial for organisations to effectively oversee their AI initiatives. It provides structure and guidance for the development, deployment, and monitoring of AI systems.
The framework outlined in the ISO standard addresses key aspects such as risk assessment, quality control, and continuous improvement. This ensures that AI projects are aligned with organisational goals and regulatory requirements.
According to KPMG, implementing a robust AI management framework can lead to improved decision-making, enhanced operational efficiency, and reduced risks associated with AI deployment.
The ISO Standard for AI is built upon key principles that ensure the ethical and responsible development and use of AI technologies. This section delves into the core aspects of transparency, accountability, and guidelines that form the foundation of the standard.
Transparency in AI systems is fundamental to building trust and understanding. It involves making AI decision-making processes clear and interpretable to both users and stakeholders.
The ISO standard emphasises the importance of explainable AI, where the reasoning behind AI-driven decisions can be understood and audited. This includes providing clear documentation on data sources, algorithms used, and potential limitations of the AI system.
Implementing transparency measures not only enhances user trust but also facilitates easier troubleshooting and improvement of AI systems. It allows for better oversight and helps in identifying and mitigating potential biases or errors in the AI’s decision-making process.
Accountability in AI systems is crucial for maintaining ethical standards and addressing potential issues. The ISO standard provides a framework for establishing clear lines of responsibility throughout the AI lifecycle.
This includes designating roles for oversight, implementing audit trails, and creating mechanisms for addressing AI-related concerns or failures. Organisations are encouraged to develop robust policies for handling AI-generated errors or unintended consequences.
By ensuring accountability, businesses can respond effectively to challenges, maintain regulatory compliance, and build stronger relationships with their stakeholders. It also provides a foundation for continuous improvement of AI systems.
The ISO standard offers comprehensive guidelines to help businesses navigate the complexities of AI implementation. These guidelines cover various aspects of AI development and deployment.
Key areas addressed include:
Ethical data collection and usage
Fairness and non-discrimination in AI algorithms
Privacy protection and data security
Regular assessment and monitoring of AI systems
Stakeholder engagement and communication
By following these guidelines, businesses can ensure their AI initiatives are aligned with best practices and ethical standards. This not only mitigates risks but also positions organisations as responsible leaders in AI innovation.
Adopting the ISO Standard for AI offers numerous benefits to organisations and provides a clear path towards certification. This section explores how the standard enhances compliance and safety, outlines the steps for achieving certification, and discusses support available for businesses on their AI implementation journey.
Adhering to the ISO Standard for AI significantly improves an organisation’s compliance posture and enhances the safety of its AI systems. It provides a structured approach to managing AI-related risks and ensuring regulatory alignment.
By implementing the standard, businesses can:
Identify and mitigate potential legal and ethical risks
Align AI practices with global regulatory requirements
Enhance data protection and privacy measures
Improve the overall safety and reliability of AI systems
Implementing the ISO Standard for AI can be a complex process, but various resources and support systems are available to assist organisations on this journey.
Many consulting firms and technology partners offer specialised services to guide businesses through the implementation and certification process. These services often include training, gap analysis, and ongoing support.
Additionally, industry forums and professional networks provide valuable platforms for knowledge sharing and best practice exchange. Engaging with these communities can offer insights into common challenges and innovative solutions in AI implementation.
Remember, the journey towards ethical AI implementation is ongoing. Continuous learning, adaptation, and improvement are key to maintaining alignment with the evolving landscape of AI technologies and standards.
Find out more…
If you would like to find out more about ethical AI standards, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
The benefits of ISO certification are evident for any organisation that implements ISO standards correctly. Having a clear stamp of approval to demonstrate that they have met the minimum levels of conformity can benefit them greatly. This is particularly the case when it comes to matters of life and death.
The Health and Safety at Work Act 1974 and the Fire Safety Act 2021 and the application of both health and safety and fire safety in the workplace also plays a key part and both are vital in helping to reduce the number of accidents that can cause death and significant injury.
This has never been more evident than in the case of the Grenfell Tower fire in 2017. Failures of fire safety, particularly regarding the cladding on the sides of the building, led to 72 deaths.
Seven years after the event, the long-awaited report into the disaster has now been published and the deputy prime minister Angela Rayner has stated that the law and regulations must be “toughened up”. This stance will have major implications for the construction sector.
In the first instance, seven companies may now undergo scrutiny for their role in the tragedy and failing to comply with existing laws. Ms Rayner name-checked product suppliers like Arconic, Kingspan and Celotex amongst others.
She told the House of Commons: “The report found that they acted with systemic dishonesty,” adding that they had not co-operated with the inquiry and that “the government will be using new powers under the Procurement Act 2023 to investigate them further.”
A total of 58 recommendations emerged from the report and the government has fully adopted 49 of them. Of the other nine, Ms Rayner said that they are being accepted “in principle,” but that some details need to be considered and consulted on.
These include the proposed single regulator for the construction industry. Ms Rayner said the government supports this, but not the idea that the regulator should have responsibility for testing or certifying products or certifying legal compliance.
What firms may expect is that ISO standards will be more important than ever and might even be updated in the light of the report, enabling companies to demonstrate a clear commitment to fire safety principles, but also placing on them an obligation to adjust to the new regulations.
The exact nature of the new regulations will be outlined after a public consultation concludes in May 2025.
While the government may not have agreed to have the regulator test products, it has committed to a tougher testing regime, with “tougher oversight of those responsible for testing and certifying, manufacturing and using construction products with serious consequences for those who break the rules.”
The government has launched a green paper on “a series of ambitious and far-reaching reforms aimed at enhancing safety, ensuring accountability, and fostering innovation and growth and therefore confidence across the construction sector.“
In time, it could be that the UK construction sector will need to adapt to prevent disasters such as Grenfell Tower in the future, but that will only happen because both the regulations and the commitment to upholding them will be in place.
Going forward, companies may find it essential to have ISO certification to demonstrate their credentials and commitments to safety in the construction industry.
Find out more…
If you would like to find out more about ISO standards, or, indeed, any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
With the COP 29 conference taking place this month in Baku, the capital of Azerbaijan, politicians and business leaders will express all sorts of hopes for new deals and action to help reduce greenhouse emissions and make the world more sustainable. The event’s slogan is “Investing in a liveable planet for all”.
However, cynics will say we have heard it all before. When COP 26 took place in Glasgow in 2021, some of the loudest voices were from campaigners outside the building like Greta Thunberg, who had made clear her views at a youth climate conference in Milan earlier that year when she famously described the rhetoric of world leaders as “blah blah blah”.
In between the scepticism of Greta and the optimism of those who see progress in various carbon-cutting agreements like reduced coal use, there is the practical reality that governments alone cannot do it all. A great many steps can be taken by businesses making authentic efforts to be greener.
However, companies can face cynicism and doubt too, with accusations of ‘greenwashing’ never far away. When this can be proven, such as a firm making claims that can be demonstrated to be false, this can lead to reputational damage.
This is where companies who not only comply with the regulations but also have a commitment to improvements through a robust environmental management system (EMS) can benefit from gaining certification to show they have done this. That is what ISO 14001 certification provides.
A central feature of ISO 14001 is that it doesn’t just acknowledge the efforts a company has made, but provides a framework for getting to the point where it has effective EMS in place, by showing the way to design the EMS and therefore meet its targets of cutting emissions and taking other steps to improve environmental performance.
These steps can include working with stakeholders on common goals, preserving and improving habitats to uphold biodiversity, more efficient use of resources, avoiding pollution and cutting energy waste. Many of these could come with cost benefits for your firm, such as lower energy bills.
Indeed, it can help steer your company in a direction where it can build partnerships and trading agreements with other companies committed to green principles, who will know from your certification that they can trust you and work with you. This can then be the catalyst for your company to enjoy sustainable growth.
Further benefits can come from highlighting the certification to ensure customers have confidence in you and your public reputation can grow as a result.
Over in Baku, politicians and diplomats will negotiate, critics will ask why the event is being held in an oil-producing state and those whose interests are still tied to fossil fuels will lobby as hard as the green campaigners.
What will not happen, of course, is any government getting its own equivalent ISO 14001. Instead, each will make a presentation on their work to meet the Paris 2015 climate targets, and the event will attempt to update this.
The result may provide more fudge than a sweet factory, which is why cynics will have much to question. But while governments may take a lot of flak, companies can protect themselves against that and also take tangible action to raise their environmental game through ISO 14001 certification.
Find out more…
If you would like to find out more about the ISO 14001 standard, how your business could benefit from implementing an Environmental Management System, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
The idea of business continuity is something that means different things to different people. There was a time when it would mostly relate to the physical premises of a company, where work could be disrupted by a major calamity, such as a fire, flood, major power outage, or terrorist attack. However, in a more interconnected world, it now extends to the online realm.
Many an organisation can face genuine threats from hackers and other cybercriminals, who may use denial-of-service attacks or malware to prevent a firm’s operations from functioning. But sometimes it can come from an internal problem, such as a software glitch.
The latter issue occurred in July this year when software firm Crowdstrike attempted a new software upload on Microsoft systems and a software bug led to massive IT outages across the globe, impacting everything from airports to banks and healthcare systems.
Such issues highlight the need for organisations to have back-up systems in place to achieve business continuity even in the face of calamity.
Whether that is about having alternative premises to work in, the ability to switch to remote working (something most firms developed the capacity to do during the pandemic lockdowns if they hadn’t already), or back-up IT systems, the best-prepared firms will be able to maintain their work, providing a better service and increasing client confidence as a result.
An ISO 22301 is a certification that shows you have met the international standard for business continuity management systems.
The purpose of attaining it is to demonstrate that you have measures in place that offer a reliable contingency when disaster strikes. In addition, it shows that you have taken clear steps to make such problems less likely to occur in the first place.
For example, when it comes to your IT systems, it could involve having strong cyber security systems and practices that make it less likely you will fall victim to cybercrime and suffer a loss of system functions as a result, as well as having measures to get your system back up and running swiftly if problems do occur.
The benefits of this are not just about being resilient in a crisis. It also means you will benefit from having a clear systemic approach to dealing with a challenging situation, so that when problems arise, you and your staff will know exactly what to do, while having better processes for managing risk.
When you have all this in place, it will increase confidence among everyone who matters, from your colleagues who can get on with their work to company shareholders who will be pleased to see earnings are not badly impacted by disruption, not to mention your clients to whom you can continue to provide a service when others might not have done.
This means the benefits of attaining an ISO 22301 are twofold. Firstly, the very act of qualifying for one means you will have established strong means of maintaining business continuity, which will benefit your business when it needs to weather the storm (sometimes literally). Secondly, having it increases the confidence others have in you.
This is why it makes sense to start working towards ISO 22301 certification today.
Find out more…
If you would like to find out more about ISO 22301, how implementing a Business Continuity Management System could benefit your business, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
Most firms will want to show their clients and customers that they are recognised as being competent and indeed excellent at what they do. Look at any company website and you will see them displaying their awards, accreditation kitemarks and memberships of trade bodies like an old soldier displays his medals.
There are some trades where certification is essential, such as Gas Safe Register membership for firms and their employees that are involved in work on gas appliances, which is required by law.
However, ISO certification is more about demonstrating standards and control than mandatory attainment of a standard to be allowed to practise.
Nonetheless, ISO certification is very much worth having, because it does provide an internationally recognised measurement of competence and standards. However, it is useful to understand the difference between certification and accreditation.
The simplest point to understand is that when it comes to ISO standards, accreditation is not something the companies being certificated attain. Rather, it applies to the bodies and organisations that can issue the certificates, which in this case includes ourselves at ISO-Cert Online.
While this accreditation is not itself a mandatory thing for certificate-issuing bodies, many organisations, such as government departments and other companies, will require that the certificate has come from an accredited body. That is the main reason why we are accredited, as that brings more benefits for you in terms of recognition.
Accreditation is also a matter of process, of course. Accreditation for individuals, for instance, comes from undertaking and passing courses to be able to practise, be they doctors, lawyers, or gas engineers. In the case of ISO certification, this is awarded based on a company demonstrating they are compliant with the requirements of their industry.
Consequently, the path to becoming certificated is a different one to accreditation. It is not about training and passing exams, a process by which you would be learning and gaining experience as you work your way up towards a particular standard. Rather, it is about being rigorously assessed to establish if your current practices meet the required standard.
This assessment, therefore, is about where you are at, not a standard you are working towards.
Of course, there is a possible scenario in which the audit shows that you have fallen short of the ISO standard you need to demonstrate to achieve certification. In that event, we would of course let you know why, and you can seek to address these issues before being assessed again.
That may be analogous to retaking an exam, except that in this case you know what the answers are. It is about whether you can achieve and demonstrate the required standard.
Of course, the assessment will be a thorough one, but that is something you should welcome. Because ISO certificates are not simply given out to anyone who wants one, your clients and customers can be assured that they are dealing with a company that has demonstrated standards that they can trust. Add in our accreditation and that trust will be all the greater.
Find out more…
If you would like to find out more about ISO standards and how implementing them could benefit your business, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
When many businesses think about ISO, they are typically looking for an accredited body to provide them with ISO 9001 certification.
They want to be certified either as a condition for a particular client, as part of a reorganisation or simply to add value to the business by celebrating a system that they have either already implemented or are in the process of implementing.
There are a lot of motivations to receive certification, but it can sometimes be easy to miss what that standardisation represents and ultimately why it matters within a business and to other businesses.
An answer to both of these questions comes, somewhat unusually, from another critical part of many businesses: a cup of tea.
There is perhaps no singular beverage that has so many variations and preferences as tea, as whilst the basic process of steeping tea leaves in water is universal, every other element from the blend to the use of teabags and the addition of milk and sugar is a matter of fierce and intense debate.
However, ISO 3103:2019 (formerly BS 6008:1980) describes a standard method of brewing and serving tea that will produce consistent results every time.
It describes two testing pots (310 ml or 150 ml) with loosely fitting lids as well as two testing bowls (380 ml and 200 ml). Both the pots and bowls are made of white porcelain (or white glazed earthenware), with a partly serrated edge.
For every 100 ml of water that will be added to the pot, 2g of tea is also placed within the pot, before that measured amount of freshly boiled water (described as similar to nearby drinking water) is added.
The tea is then brewed for six minutes before being poured into the bowl, with 5ml (or 2.5ml for a smaller bowl) milk added beforehand (although alternative suggestions are made for adding milk after).
The resulting standard won an Ig Nobel Prize and serves as a perfect example of how standards can often be misinterpreted as a prescriptive method towards a platonic ideal for the object, method or system being standardised.
However, this somewhat misses the point, as ISO 3103:2019 is not intended to make the best cup of tea or a “perfect” cup of tea by the standards of a tea drinker, but is instead intended to create a standard cup of tea that is relatively easily reproducible.
The reason for this is the same reason why no specific type or blend of tea is described in the standard. It is designed for tea tasting and for making sensory comparisons.
Many criticisms of the process, such as no prewarming of the pot, a brewing time that is relatively lengthy compared to the typical three-minute brewing times used when brewing a tea bag, and pouring milk in before tea largely misses the point.
These are not cups that are made to be enjoyed, but ones that create a benchmark for meaningful analysis and studies, such as taste testing or quality control.
On that same token, ISO certification means adopting a universal set of standards and protocols so that other businesses and customers understand how an order is managed by your company.
Find out more…
If you would like to find out more about ISO standards and how implementing them could benefit your business, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
When businesses are interested in ISO certification, the fastest way to achieve this is through a dedicated online service that will help them meet the necessary quality management standards.
When businesses are looking for certification, they are typically thinking about the ISO 9000 family, which is a set of five quality management systems (QMS) that ensure that businesses are meeting their regulatory responsibilities, whilst also ensuring they are keeping up with the demands of customers and stakeholders alike.
Of the five ISO 9000 QMS standards, the one that most companies are looking for is ISO 9001:2015, often known simply as “ISO 9001”, “ISO 9000” or even simply “ISO”.
The standard itself is based around a 30-page set of requirements but its fundamental focus is based on seven quality management principles (QMP) which form or at least should form a foundation for how a business is managed and operated.
Here are the seven and why they matter.
The first QMP standard is perhaps the most obvious one. As the late entrepreneur and businessman Jack Tramiel put it, businesses are there to serve the customer.
Without customers, businesses simply cannot exist, and with that in mind, companies focused on ISO 9001 should be mindful not only of customer needs right now but the future of their needs in the future.
The priority should be to meet the standards of the customer and serve them, ensuring that the customer’s expectations are understood so they can be delivered upon effectively and efficiently.
One of the most critical and misunderstood aspects of many businesses is structure, hierarchy and leadership, as well as the role of leaders in organisations of varying scales.
Leaders need to be the ones to form and shape a united direction and purpose of any organisation and be able to lead a wide range of disparate teams in the same direction to achieve the overarching mission of the company.
Companies are ultimately collectives of diverse, skilled individuals, and ultimately no company succeeds without people who are able to do the job they are employed to, are empowered and recognised for their abilities, and buy into the overall goals of the organisation.
Without people on board, you do not have a company.
Business activities are typically a series of interrelated processes that work together to create an overall system, and once a business fully understands this, it can manage and continually improve these processes to achieve consistent output results.
Perfection is an overall goal, but not one that is achievable. There is always room for improvement, and an eternal goal for any organisation is to keep getting better, streamline processes and get the greatest return out of every part of the business.
Data dominates the business world, and whilst one should avoid discounting anything that cannot be quantified, decisions should be made based on effective, objective analysis to as much pertinent information as possible.
No business exists in a vacuum. Virtually every company has contractors, suppliers, service providers and other stakeholders that are part of symbiotic, interdependent business relationships. It is important to see the value in these relationships and foster them to ensure everyone thrives.
Find out more…
If you would like to find out more about ISO standards and how implementing them could benefit your business, or any of the other services we offer here at ISO-Cert Online, please contact us on 0333 014 7720 or email info@isocertonline.net.
Do you hold, or are you thinking of seeking, ISO 9001 certification? If so, you’ll want to know about the results of a recent meeting of the ISO/TC 176/SC 2. The ISO subcommittee for Quality Systems convened for a ballot about an update on revisions to ISO 9001:2026.
The much-anticipated vote determined whether or not a revision of the ISO 9001 standard should go ahead sooner rather than later. Although the next scheduled review is not until 2026, the committee voted to start a revision now.
The comforting news is that any changes won’t happen quickly, despite this decision. Before any changes can take place:
For now, you don’t need to do anything. Even when the revisions to ISO 9001:2026 are introduced, you won’t have to adopt it straightaway. Once it is rolled out, we expect that certified organisations will have up to three years to switch. At least, that was grace period available after the last update (from ISO 9001:2008 to ISO 9001:2026). This would seem a reasonable transition period in advance of the current version becoming obsolete.
Rest assured, we will update our ISO certified clients on any further developments which will affect your ISO 9001 certification.
For more information on ISO-Cert Online’s services or to discuss your requirements please contact us on 0333 014 7720 or email info@isocertonline.net.
How can ISO 9001 certification help you to win more tenders? Read our latest blog which highlights how some of the benefits of being ISO certified can give you a real advantage against your competitors when bidding for new business.…
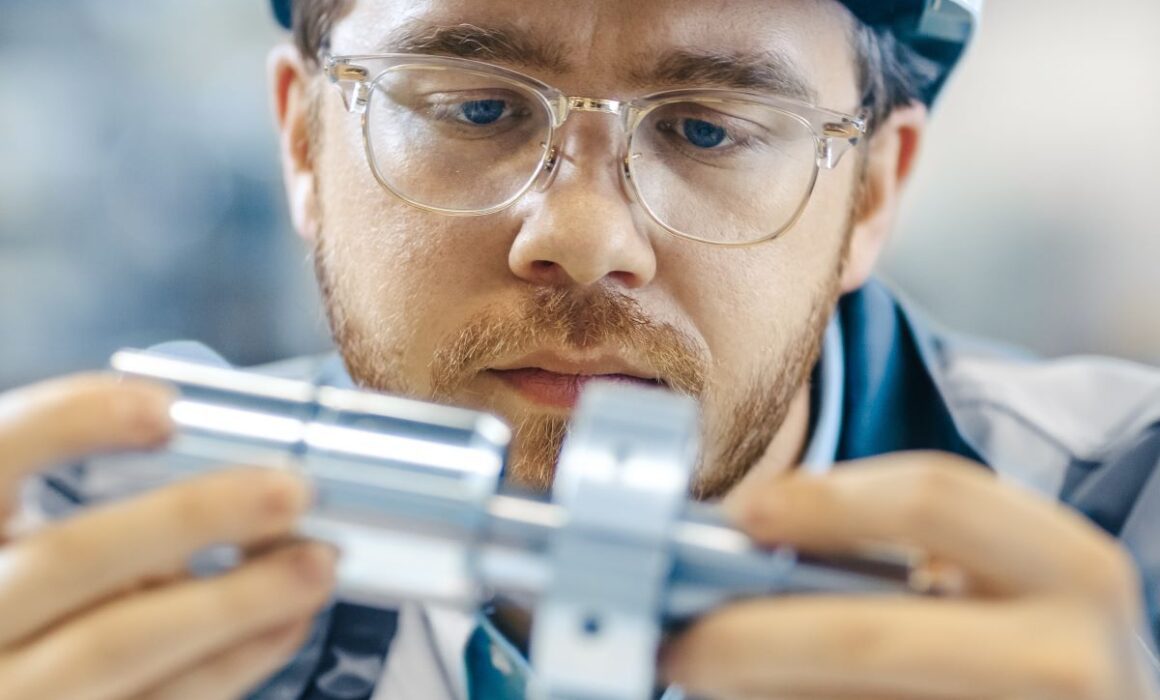
Over the last hundred years, and at an ever-increasing speed of late, advancements in technology have helped the manufacturing industry become safer, faster, and more cost-efficient. And whether you’re a manufacturer, retailer or consumer, product safety will be high on your agenda. In this article, we will consider the risks of failing to ensure product safety. And we will look at how ISO certification helps ensure product safety.
As a manufacturer, distributor, or retailer, it’s your responsibility to make sure that products are safe. Both for consumers to use, and for following the legal requirements in relation to packaging and labelling.
Consumer harm and injuries: The most critical risk is the potential harm and injuries caused to consumers. Unsafe products can lead to accidents, injuries, illnesses, or even fatalities.
Manufacturer liability: Manufacturers which fall short in their duty of care to customers are frequently held responsible for injuries, damages or losses caused by their unsafe products. This can result in legal consequences, financial penalties, and direct compensation claims. Where these occur in the public eye, considerable damage can be done to their reputation. In the most serious cases, businesses have even faced bankruptcy.
Regulatory penalties: Regulatory bodies, for example the Health and Safety Executive or the Food Standards Agency, have the authority to impose penalties, fines, and sanctions on both manufacturers and retailers who fail to meet product safety standards. Depending on the severity to consumers of the case, these can be significant. And can not only impact a company’s financial stability and credibility, but also its ability to operate in the market. The internet provides plenty of examples of businesses which have failed in their duty of care to customers and paid a hefty price.
Loss of consumer trust: Where products are purchased via a retailer, a safety breach can negatively impact on more than one business – the manufacturer and the retailer. If confidence in a brand is damaged then the knock-on effects can be significant. They can include decreased sales, loss of market share, and long-term harm to the company’s reputation. Increasingly, consumers are aware of their power to influence others. And it has been known for them to air their grievances with businesses publicly. Often, most effectively on social media, in a bid to make companies accountable for their failings.
Product recalls and replacements: In cases where safety hazards are identified, manufacturers and retailers may need to work together to initiate product recalls or replacements. This process is costly and time-consuming. It can result in financial losses due to product retrieval and disposal, as well as potential reputational damage.
Employee wellbeing: No legitimate business sets outs with the intention of harming the public. Where serious failings occur, the impact on its own staff can be profound. It is essential for businesses to be transparent with their employees. They should explain learnings and communicate improvements which will mitigate the risk of a similar incident happening again. Similarly, businesses may wish to arm staff with advice on how to manage negative publicity.
The International Organization for Standardization has developed a range of standards regarding product safety. These include ISO 9001 (quality management), ISO 22000 (food safety management) and ISO 13485 (medical device quality management). These standards give detailed rules on how to ensure product safety through risk assessment, hazard identification, as well as control measures.
Businesses are able to acquire ISO certification once they have established an appropriate management system and have been successfully audited. Thus demonstrating that their products are safe for use or consumption. How ISO certification helps ensure product safety requires the following:
Using ISO certification companies need to conduct risk assessments and identify potential hazards in relation to their products. This should involve evaluating the potential dangers that might arise. Typically these are found in design inconsistencies, production processes, packaging techniques, labelling and usage instructions, and during distribution. With the information obtained from the assessment process, companies then implement effective countermeasures geared towards reducing such risks. Thereby ensuring that their products are safe for use or consumption.
As part of ISO certification, businesses must implement control measures aimed at mitigating the potential risks associated with their products. These measures may encompass implementing quality control processes, introducing testing procedures, and also involve committing to regular inspection routines. All resulting in ensuring that products meet safety standards and comply with regulatory requirements.
One of the main benefits of ISO certification lies in its purpose to drive ongoing and continuous improvement. So, the journey doesn’t end when you receive your certificate! To maintain certification, businesses should conduct regular audits. These will evaluate whether their management systems are still effective. In so doing, companies can be confident that their processes and procedures are robust, relevant, and always improving to ensure ongoing product safety for consumers.
“Many of our clients come to us because they are looking for a straightforward, common-sense approach to how ISO certification can help ensure product safety. When nothing short of excellence will do, ISO certification provides that framework they need. Helping them to demonstrate their commitment to the rigorous standards that build trust, safeguard their customers, and keep their reputation intact.”
Claire Howard, Director of ISO-Cert Online Ltd
For more information on ISO-Cert Online’s services or to discuss your requirements please contact us on 0333 014 7720 or email info@isocertonline.net.
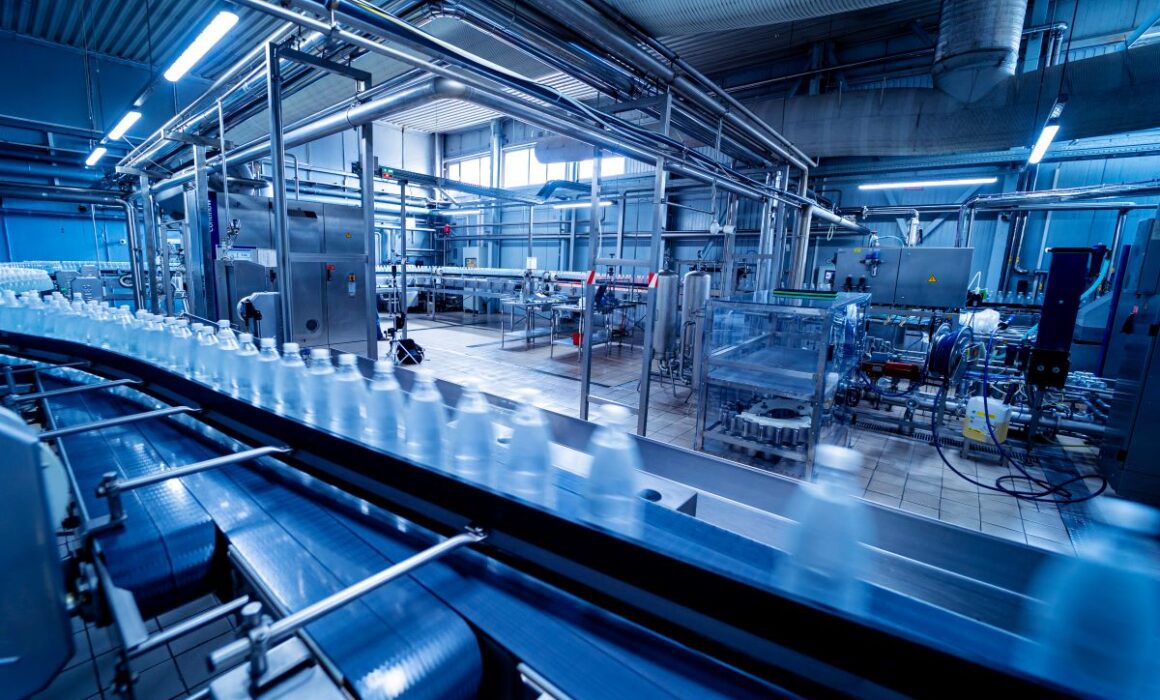
Globally, the food and drink manufacturing industry is one of the most strictly controlled industries. It has regulations governing everything from food safety and production processes through to labelling and packaging. What’s more, quality and safety levels must be maintained at all times across supply chains. ISO certification provides those in the food industry with a comprehensive framework to make meeting these requirements more manageable. So, in this article, we’ll explore the importance of ISO certification in the food industry.
Regardless of the size of an organisation or its product, all food producers and distributors have a responsibility to manage the safety of their products and the well-being of their consumers. Compliance with current food safety standards, potentially across different continents of the world, is essential but can be complex. So the International Organization for Standardization developed ISO 22000 for use within the global food supply chain. Its aim was to bring people food that they can trust.
The consequences of unsafe food can be serious. So implementing a food safety management system (FSMS), such as ISO 22000, is essential. It guides you through how to make careful risk assessments as well as manage hazards, monitor processes, and apply controls. By achieving certification, firms clearly establish themselves as advocates for sustainability and safe practices. Also significantly reducing the likelihood of foodborne illness outbreaks – e.g. Norovirus, Salmonella and Listeria. Such outbreaks are not only unpleasant for consumers. They can lead to product recalls, reputational damage, the risk of penalties and fines. Moreover, in very serious instances, company closure.
Although ISO 22000 is specifically relevant to the food industry, there are a range of other ISO standards which are popular and appropriate for the sector.
ISO 9001: The most common ISO standard supports businesses in improving their quality management processes. This leads to food products being high quality and meeting customer requirements.
ISO 14001: Consumers are placing greater value on the provenance of what they eat and how it’s packaged. So implementing an environmental management system encourages businesses to improve their environmental impact and operate sustainably.
ISO 45001: Regardless of your industry, you should want to provide a safe workplace for your staff. In food manufacturing specifically, heavy machinery used in the production process can pose a risk if not used correctly or safely. An occupational health and safety management system provides a framework for managing safety at work. This improves the protection of your staff in their day-to-day roles.
“Food is essential in our lives – not just for sustenance but for socialising and cultural identity. Whether your company is involved in the production, processing, and distribution of food products, or you supply ingredients or packaging materials to the food industry, ISO standards enable you to uphold the highest standards, demonstrating your commitment to delivering reliable and trustworthy products to consumers.”
Claire Howard, Director of ISO-Cert Online Ltd
For more information on ISO-Cert Online’s services or to discuss your requirements please contact us on 0333 014 7720 or email info@isocertonline.net.


Copyright © 2025 ISO-Cert Online Ltd. All Rights Reserved

Recent Comments